How Passkeys Work: Sign-In Security and Recovery Planning
2026-11-03 · Updated: 2026-11-04 · 3 min read
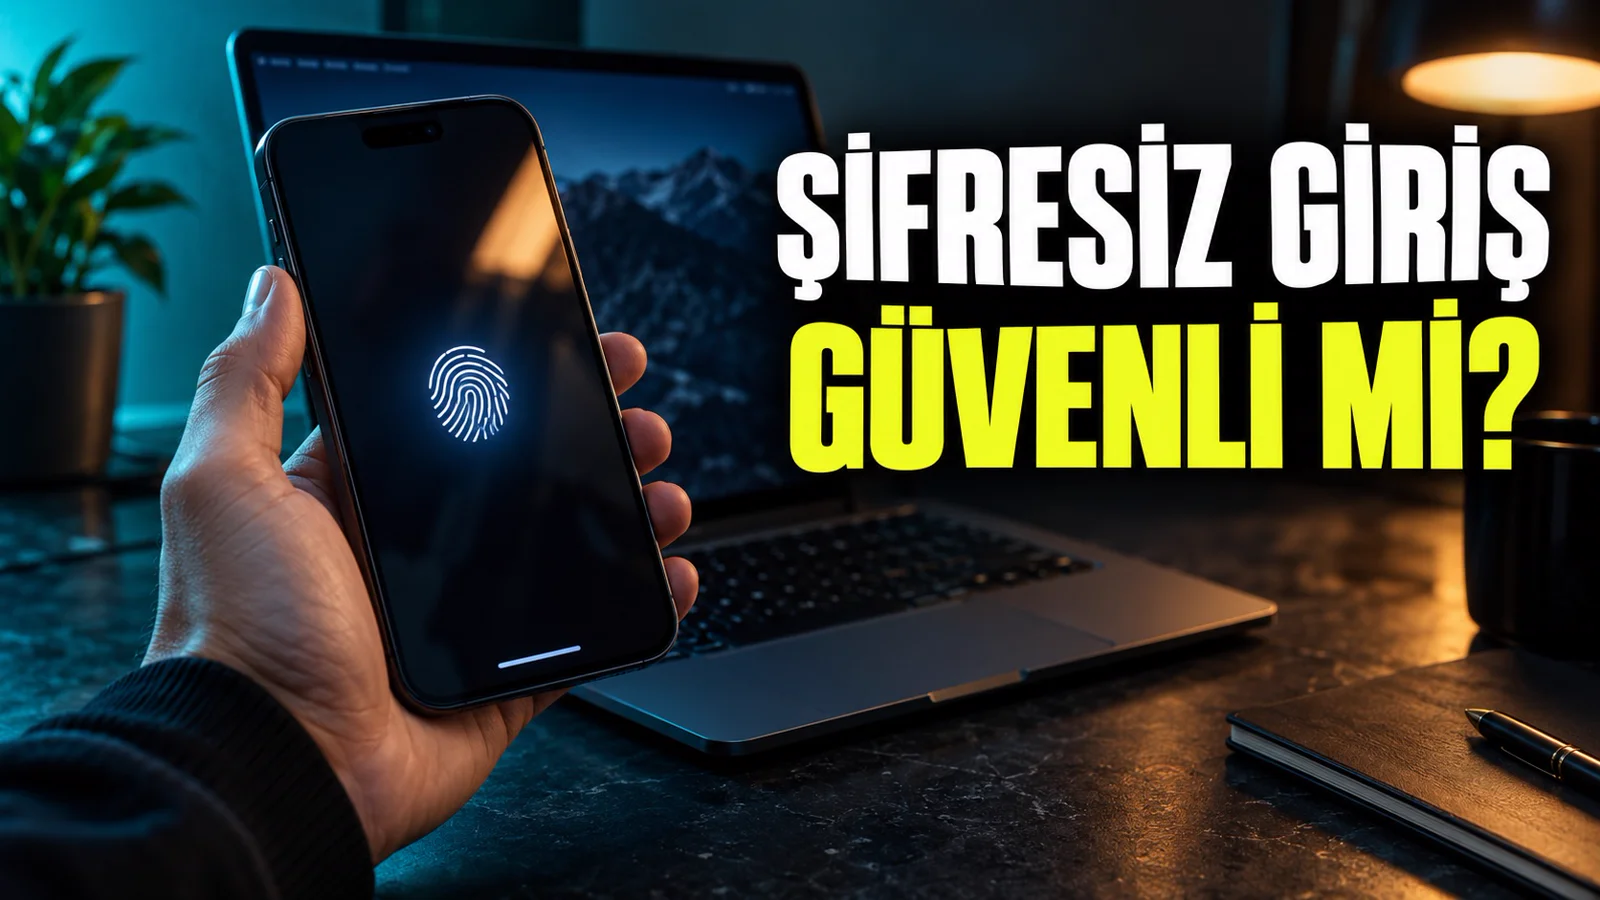
A passkey lets a supported service verify a cryptographic sign-in rather than asking you to send a reusable password. You may approve the sign-in with a device PIN or biometric check. The important distinction is between unlocking the credential locally and proving your identity to the service.
Understand the basic sign-in model
FIDO describes passkeys as based on public-key cryptography. The service holds a public key, while the corresponding private credential is used through your authenticator. The exact storage and synchronisation arrangements depend on the platform and provider.
This is different from typing the same secret into a website. The sign-in is tied to the intended service, which is an important part of resistance to phishing. It does not make every part of an account immune to abuse or remove the need to secure devices and recovery methods.
Your fingerprint is not the website password
A fingerprint, face check or device PIN can authorise use of the passkey locally. The website is not simply receiving a copy of your fingerprint as a replacement password. Keep local device access and the website's verification process conceptually separate.
For your own setup, read how the platform stores or syncs credentials and which devices can use them. Avoid assuming that all passkeys live only on one phone or that every service supports the same recovery path.
Examine the whole account setup
Before enabling a new sign-in method, inspect the service's account security page. Identify existing passwords, recovery email, phone numbers, trusted devices and other authenticators. Security depends on the remaining access paths as well as the strongest one.
Update outdated recovery details using the service's documented process. Keep a record of which devices and accounts are involved without publishing private recovery information in a shared checklist. A forgotten dependency can become visible only when the main phone is lost.
Plan for a missing or replaced device
Ask how you would sign in if the usual phone were unavailable. Check whether the provider supports synchronised access, another registered authenticator or a documented recovery procedure. The right answer is provider-specific, not one universal sequence.
Where supported, establish an additional approved way in before relying on a single device. Do not delete existing working access until you understand the new arrangement and have verified it under the provider's instructions. Account recovery should be planned while you still have access.
Test ordinary use without risking lockout
After setup, confirm that the intended device can sign in and that the account shows the expected credential. Try a documented secondary route if the service provides one. Keep any recovery material in an appropriate secure place separate from public notes.
Do not infer successful recovery merely because ordinary sign-in worked once. Those are different tasks. A useful checklist names both the normal path and the fallback path, including which provider account is needed for each.
Keep the claim proportionate
Passkeys improve the sign-in model, but they are not a promise that an account can never be compromised. Device access, recovery channels, sessions and service behaviour still matter. The accompanying video introduces the distinction; this guide expands the operational checks.
Consult FIDO's passkey explanation and your platform's current documentation for implementation details. The practical goal is a supported sign-in method with a recovery route you understand, rather than simply removing a password and hoping access will remain available.
Sources and scope
Related videos
The linked videos use Turkish narration. This article provides the English explanation of the same topic and assumptions.
Edited by GKN Labs. Editorial update: 4 November 2026. Cover and explanatory visuals are illustrative, not evidence of product testing or measurement.
Related
 Business
How Long to Upload 1 TB? Use Upload Speed, Not Download
Calculate 1 TB cloud upload time from Mbps, distinguish bits from bytes and account for daily operating hours, interruptions and real service limits.
 Business
NAS Electricity Cost: Calculate 24/7 Energy Use
Calculate annual NAS electricity use from watts or measured kWh, understand adapter ratings and add energy to a complete storage-cost comparison.
NAS vs Cloud Storage: Compare Three-Year Ownership Costs
Compare NAS and cloud storage with a three-year cost example, usable RAID capacity, electricity, backup requirements and a practical decision checklist.
Turkish narration. Learn how passkeys use public-key sign-in, why biometrics stay on the device and what to check before relying on a phone for account recovery. Read the companion English guide for the same topic and assumptions.